Opensesame
Simple authentication and user management service.
OpenSesame
A self-built authentication and user-management service, with roles and permissions baked in.
Live app · Frontend source · Backend source
Every product eventually needs to answer “who is this user, and what are they allowed to do.” Instead of reaching for a third-party auth provider, I built that piece myself: a JWT-based auth API paired with an admin console to manage users, roles, and fine-grained permissions.
What it does
- Log in / log out with JWT issued as httpOnly cookies — no tokens sitting in localStorage
- Two-layer access control: coarse
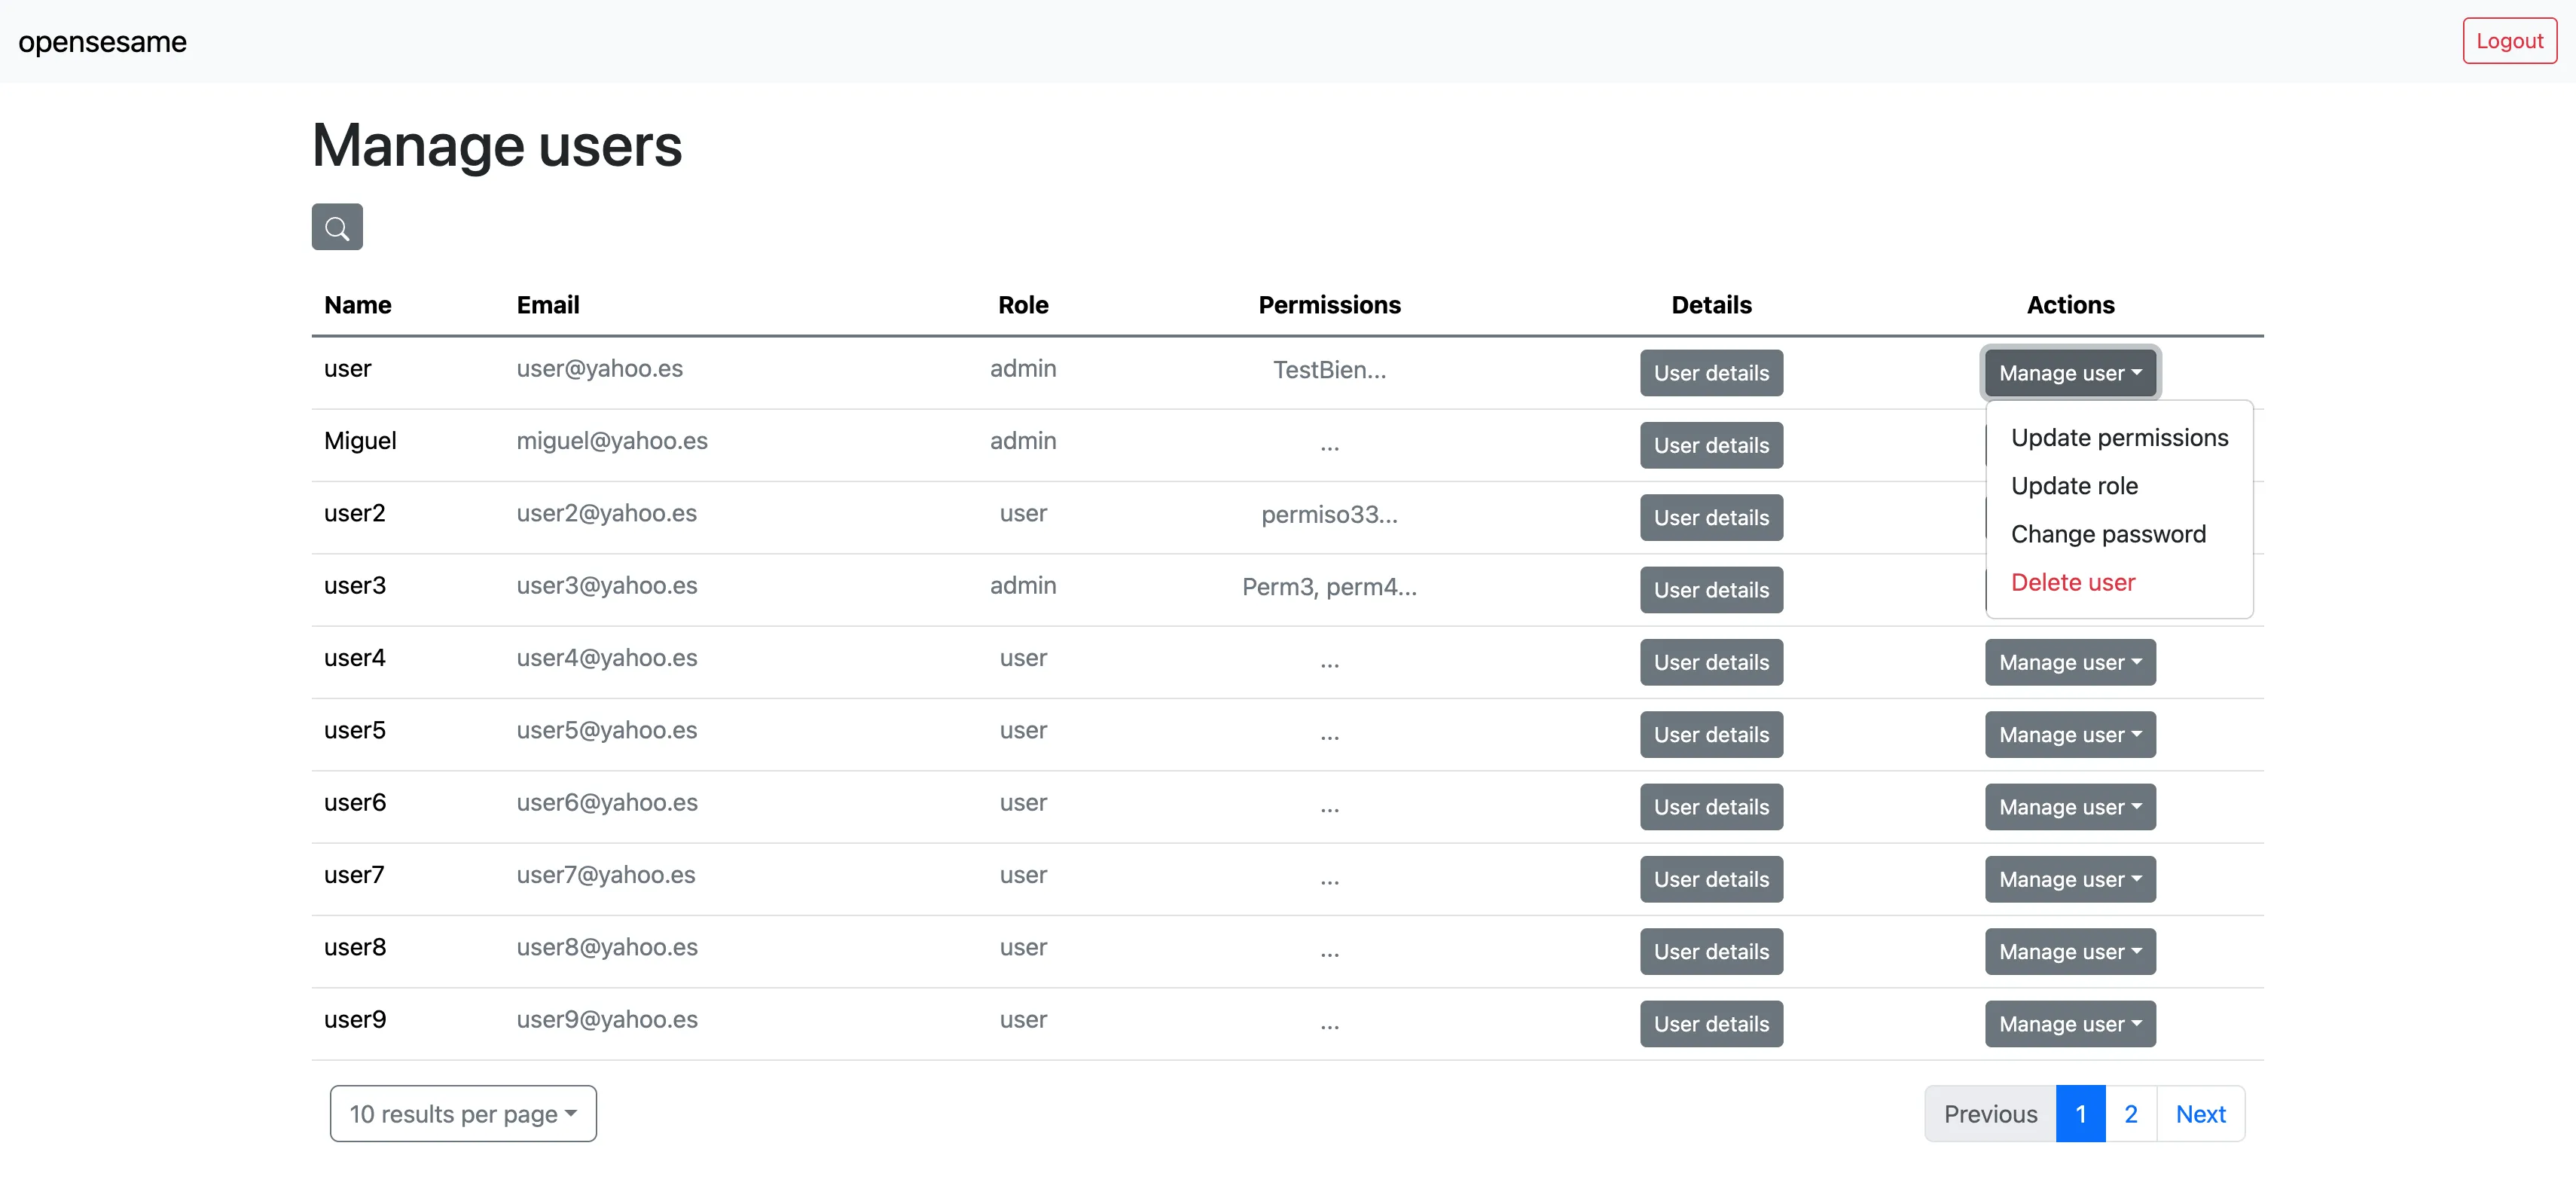
admin/userroles plus per-user granular permissions - Admin console to list, search, and inspect users
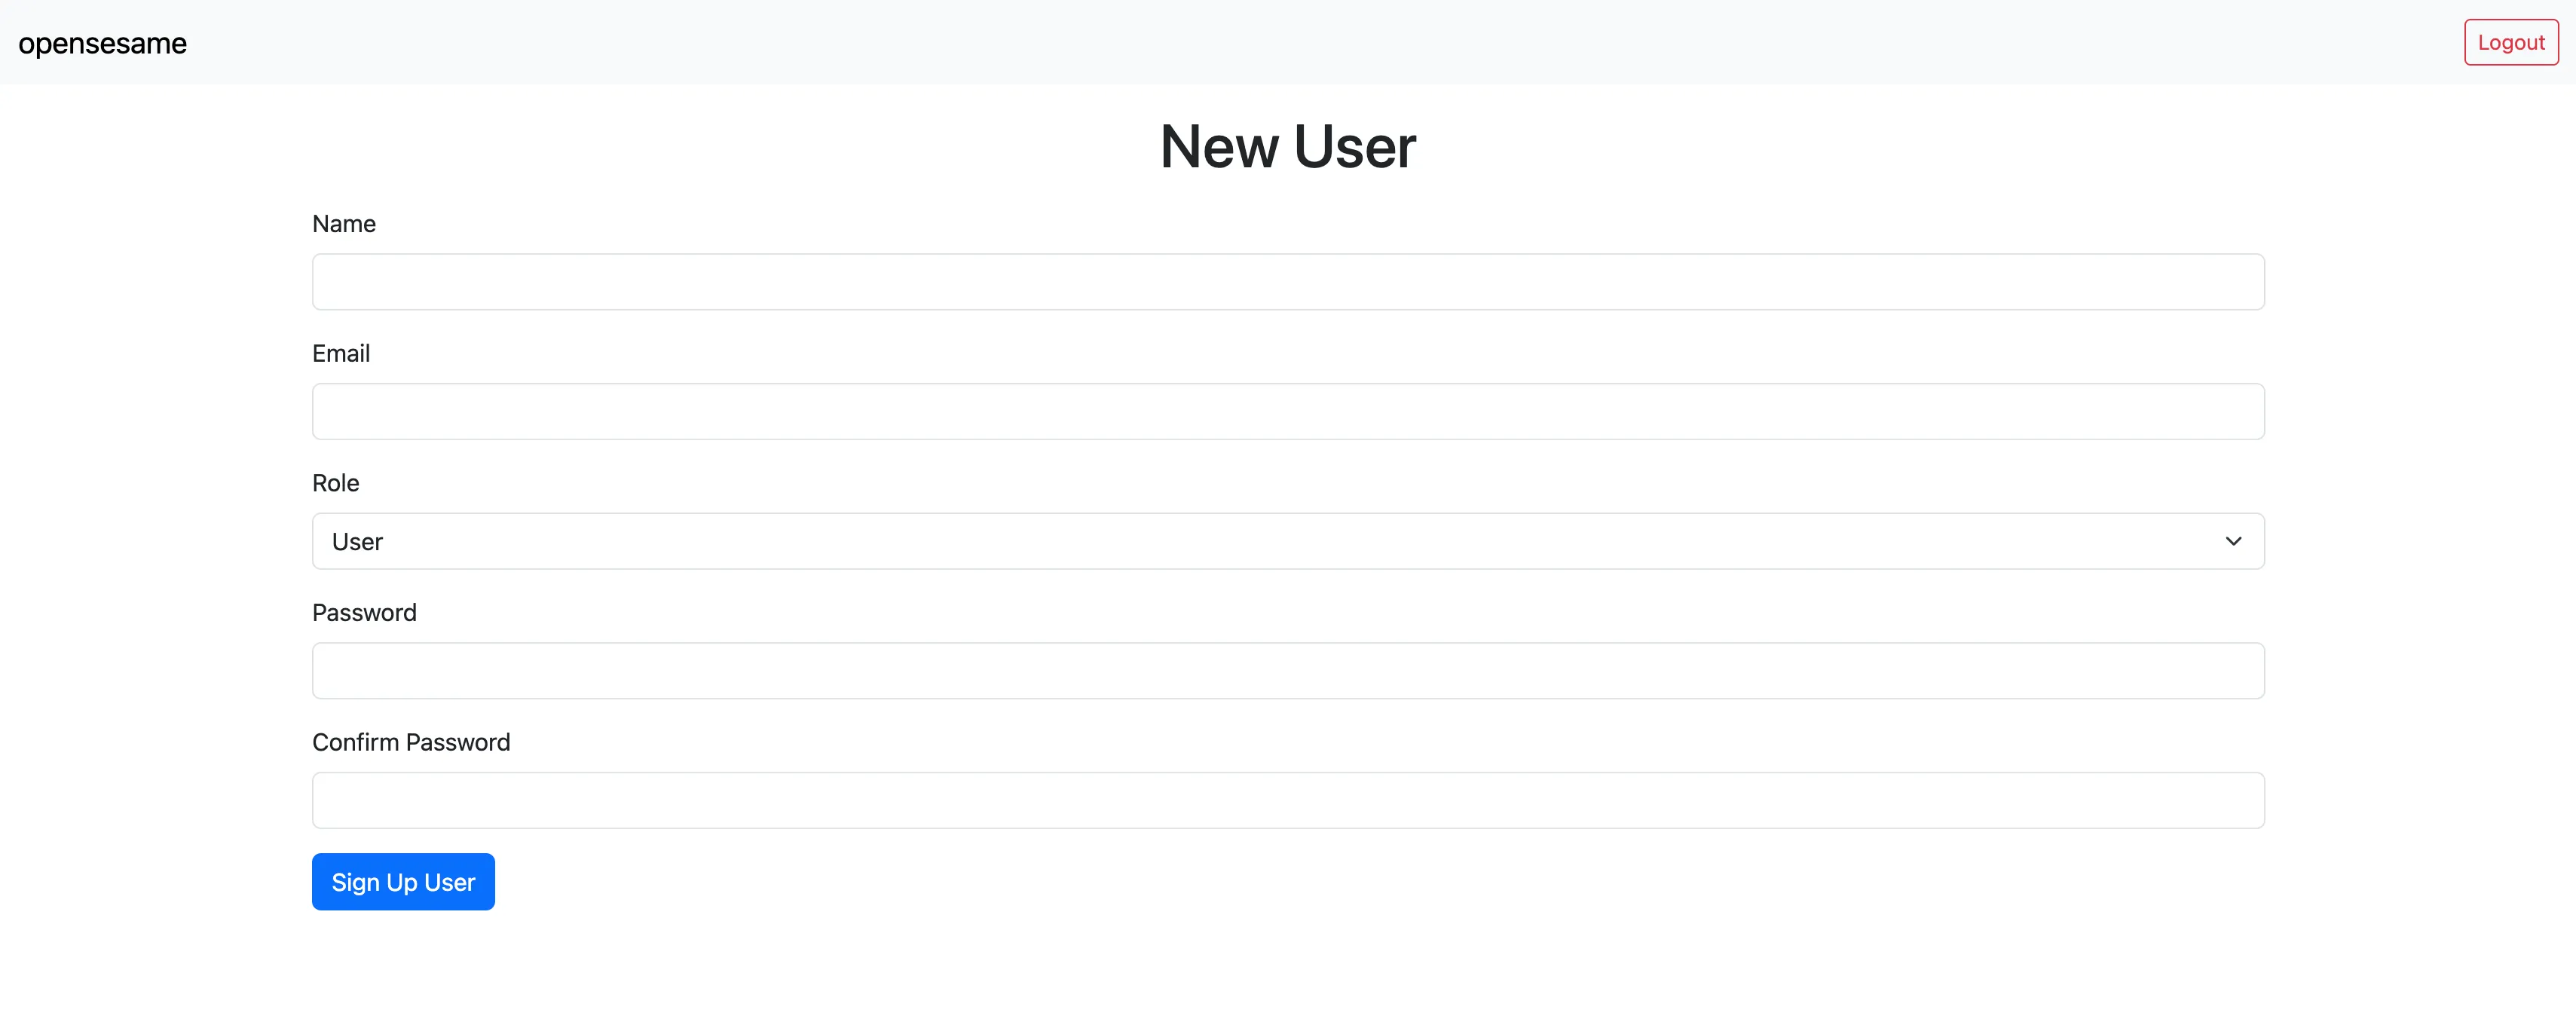
- Admins provision new accounts, force password resets, and grant or revoke roles/permissions
- Users can change their own password once logged in
How it’s built
React 19 + TypeScript frontend (React Router v7, Context-based state, Axios over cookie auth) talking to a Node/Express + TypeScript API backed by MongoDB. The API is hardened with helmet, CORS allow-listing, rate limiting, request validation, and bcrypt password hashing.
- One-command full-stack demo — a Docker Compose stack spins up MongoDB, the auth API, and the frontend together, seeded with a demo admin user, so anyone can try the whole thing locally in minutes.
- CI & security gate — every push and PR runs a full verify pipeline (audit, lint, typecheck, test, build) across both repos, plus gitleaks secret scanning before anything merges.
Try the live app, or spin up the Docker demo yourself.